// resources · author
Chuck Tommey
Co-Founder and Chief Advisory Officer, Hillstrong Group Security
Articles (8)
-
The Critical Infrastructure Hat: When Your Asset Belongs to the Grid
Critical infrastructure incident clocks compared: one hour under NERC CIP-008-6, 12 under SOCI, 24 under NIS2, and why to build for the tightest one.
-
The Operator Hat: The Service You Sell Is the Attack Path You Own
How OEM service access becomes a multi-customer attack path, what NIS2 Article 21 and service contracts demand, and three fixes, from tenant isolation to MFA.
-
The Product Hat: Every Unit You Shipped Is Still Your Problem
What the EU Cyber Resilience Act means for connected hardware: 24-hour vulnerability reports, an SBOM, five-year support, and the September 2026 deadline.
-
The Enterprise Hat: When Cyber Risk Reaches the Boardroom
How NIS2 Article 20, SEC Item 1.05, and the SOCI Act moved cyber risk to the board, from turnover-based fines to management bans, and three moves to make.
-
Tie OT Security to What the Plant Must Deliver
OT security should serve the plant's mission. Protect uptime with compensating controls, measure operational outcomes, and anchor the work in an OT GRC program.
-
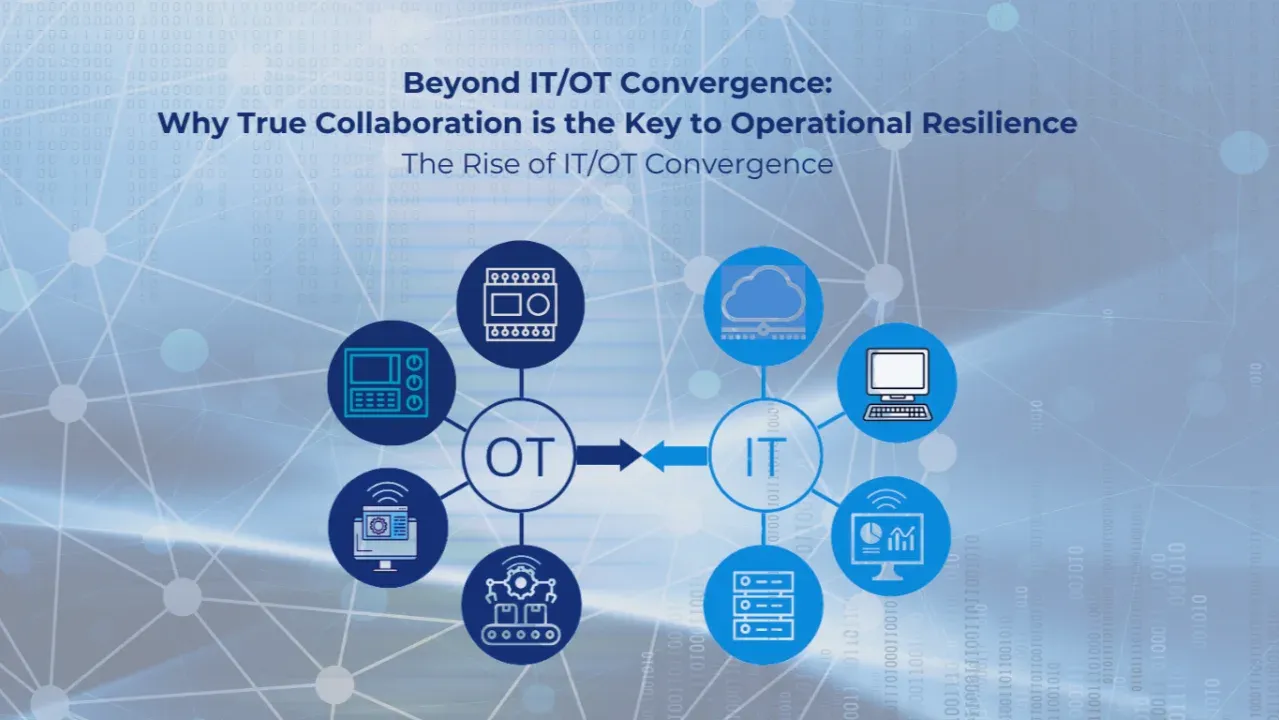
Operational Resilience Depends on IT and OT Working Together
IT/OT convergence widens the attack surface without making plants safer. Four collaboration steps close the gap, starting with an OT-specific GRC program.
-
Breaking Down Silos: Why IT and OT Must Work Together on Cybersecurity
IT protects data and OT protects uptime and safety. Four steps align both teams, from a shared framework and joint risk reviews to OT-specific security rules.
-
How IT and OT Collaboration Strengthens OT Cybersecurity
Weak GRC maturity stalls many OT security programs. OT teams can borrow IT's ISO 27001 experience and partner with plant safety to build OT GRC faster.
Talk it through with a practitioner
Book a 30-minute consultation with a senior OT security practitioner about your plants.